11/11/2026
Detect vulnerability scan failures that remain hidden behind successful jobs by reconciling expected asset-method evidence and testing each control stage.
silent scan failuresvulnerability scanner healthscan coverage gapsvulnerability operationsLayer8 Sentinel
11/11/2026
Build vulnerability scanner health monitoring around scope, assessment depth, execution, identity, and evidence delivery instead of relying on job status alone.
vulnerability scanner healthscan monitoringvulnerability scan coveragesecurity operationsLayer8 Sentinel
11/9/2026
Conduct an evidence-based AI ticket routing post-incident review that turns failures into verified prevention, detection, containment, and recovery controls.
AI ticket routing post-incident reviewrouting incident analysisservice desk governancecorrective actionsLayer8 Triage
11/9/2026
Build an executable AI ticket routing incident runbook with clear entry conditions, scoped containment, evidence capture, diagnostics, and recovery gates.
AI ticket routing runbookincident runbookservice desk operationsrouting containmentLayer8 Triage
11/9/2026
A practical framework for detecting, containing, investigating, and recovering from AI ticket routing incidents without losing decision evidence.
AI ticket routing incident responseservice desk incident managementrouting governanceAI triage operationsLayer8 Triage
11/6/2026
Detect and investigate unauthorized compliance evidence deletion by correlating activity, authorization, lineage, recovery, and downstream audit impact.
evidence deletioncompliance evidence integrityincident investigationaudit trailevidence recoveryLayer8 Compliance
11/6/2026
Run a defensible permission review across compliance evidence repositories by resolving effective access, testing role policy, and verifying remediation.
permission reviewcompliance evidence accessleast privilegeevidence repositoryaccess certificationLayer8 Compliance
11/6/2026
Build an operational access governance model for compliance evidence repositories, including role design, destructive-action controls, reviews, and investigation evidence.
compliance evidence accessevidence governanceleast privilegeaudit evidenceGRC operationsLayer8 Compliance
11/4/2026
Detect explicit and hidden vulnerability scan exclusions, validate their authority, measure affected assets and methods, and restore trustworthy evidence.
scan exclusionsvulnerability scan coverageconfiguration driftexception managementLayer8 Sentinel
11/4/2026
Build a control-focused vulnerability scanner baseline that captures scope, assessment depth, execution, authentication, identity, and evidence requirements.
scanner baselinevulnerability scanner configurationconfiguration managementcredentialed scanningLayer8 Sentinel
11/4/2026
Manage vulnerability scanner configuration drift by baselining control-defining settings, detecting operational changes, and verifying corrections with fresh evidence.
vulnerability scanner configurationconfiguration driftvulnerability scan coveragescan operationsLayer8 Sentinel
11/2/2026
Design production alerts for routing drift using safety invariants, segmented baselines, minimum volumes, severity, and response runbooks.
AI ticket routing driftrouting alertsservice desk monitoringAI triage governancerouting observabilityLayer8 Triage
11/2/2026
Build a production dashboard that connects routing health, policy actions, corrections, operational impact, and event-level evidence.
AI routing dashboardticket routing qualityservice desk metricsrouting analyticsAI triage observabilityLayer8 Triage
11/2/2026
A practical framework for observing AI ticket routing decisions, measuring production quality, and investigating unsafe changes.
AI ticket routing observabilityservice desk analyticsrouting qualityAI triage governanceticket automationLayer8 Triage
10/30/2026
Use hashes, immutable object versions, and manifests to verify that reviewed compliance evidence has not been silently altered or replaced.
compliance evidence integritycryptographic hashesimmutable evidenceaudit trailevidence versioningLayer8 Compliance
10/30/2026
Define a practical provenance metadata schema that makes compliance evidence traceable from authoritative source through review and retention.
evidence provenance metadataaudit evidencecompliance evidence lineageevidence schemaGRC operationsLayer8 Compliance
10/30/2026
Build an operational chain of custody for compliance evidence from source collection through transformation, review, retention, and audit delivery.
compliance evidence lineagechain of custodyevidence provenanceaudit evidenceGRC operationsLayer8 Compliance
10/28/2026
Measure vulnerability scan coverage for autoscaling instances, containers, and short-lived cloud workloads without relying on misleading point-in-time host counts.
ephemeral assetscloud securityvulnerability scan coveragecontainer scanningLayer8 Sentinel
10/28/2026
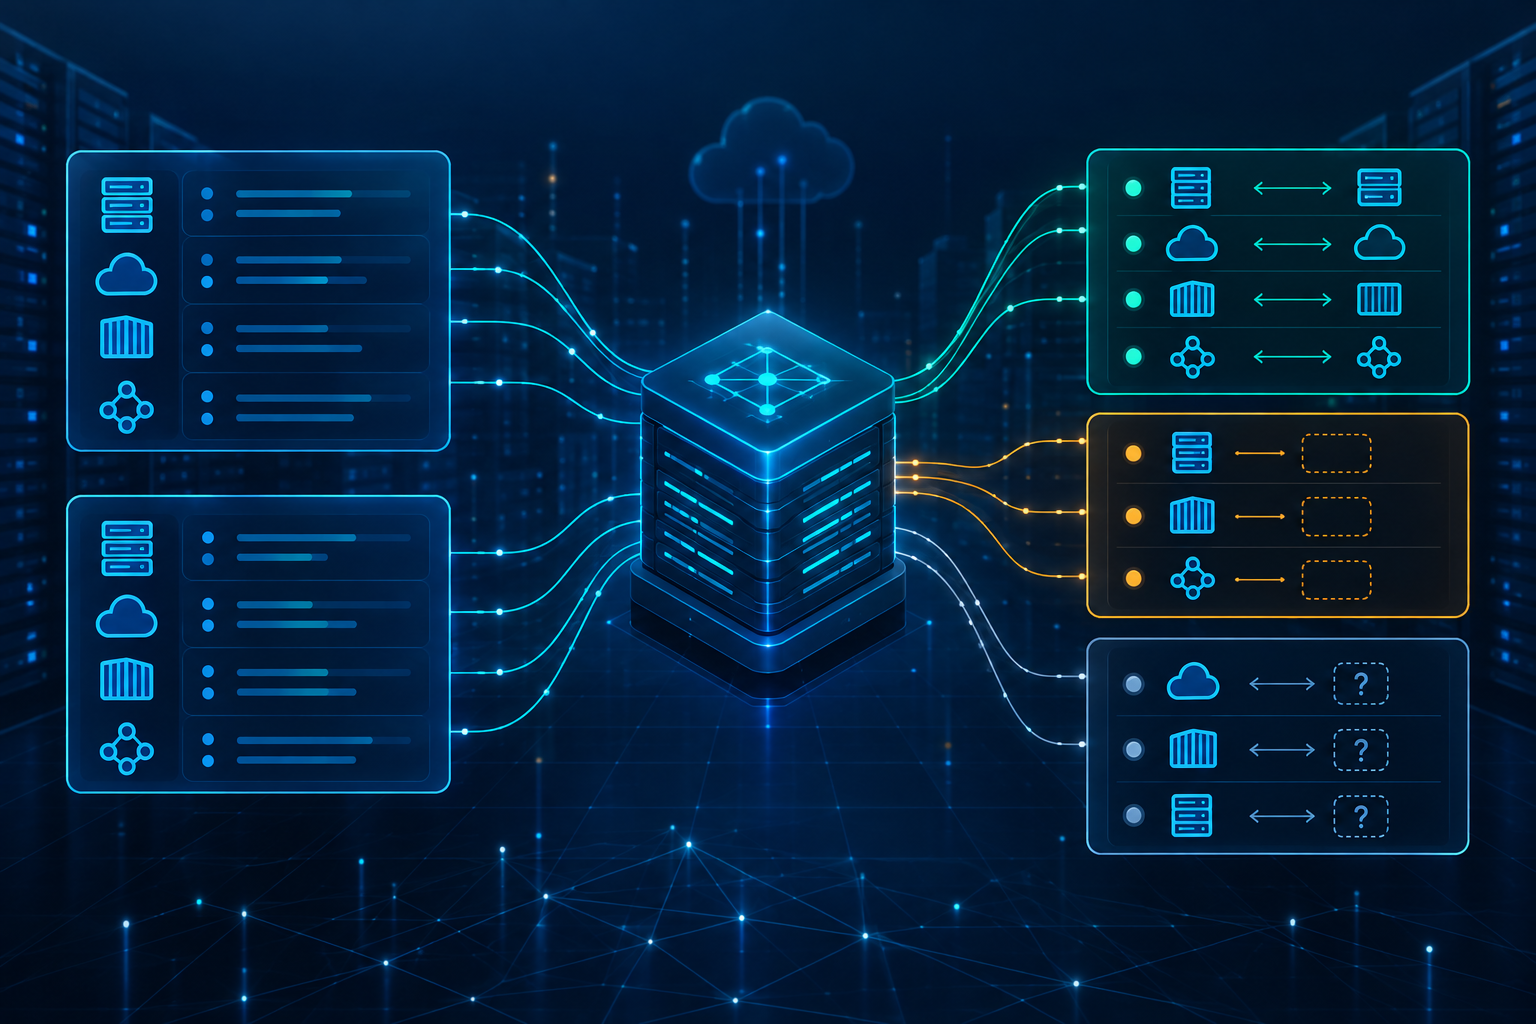
Reconcile vulnerability scanner targets with authoritative asset inventory to find missed systems, stale records, ambiguous identities, and invalid scope.
asset reconciliationscan targetsasset inventoryvulnerability scan coverageLayer8 Sentinel