How to Review Compliance Evidence Repository Permissions
Run a defensible permission review across compliance evidence repositories by resolving effective access, testing role policy, and verifying remediation.
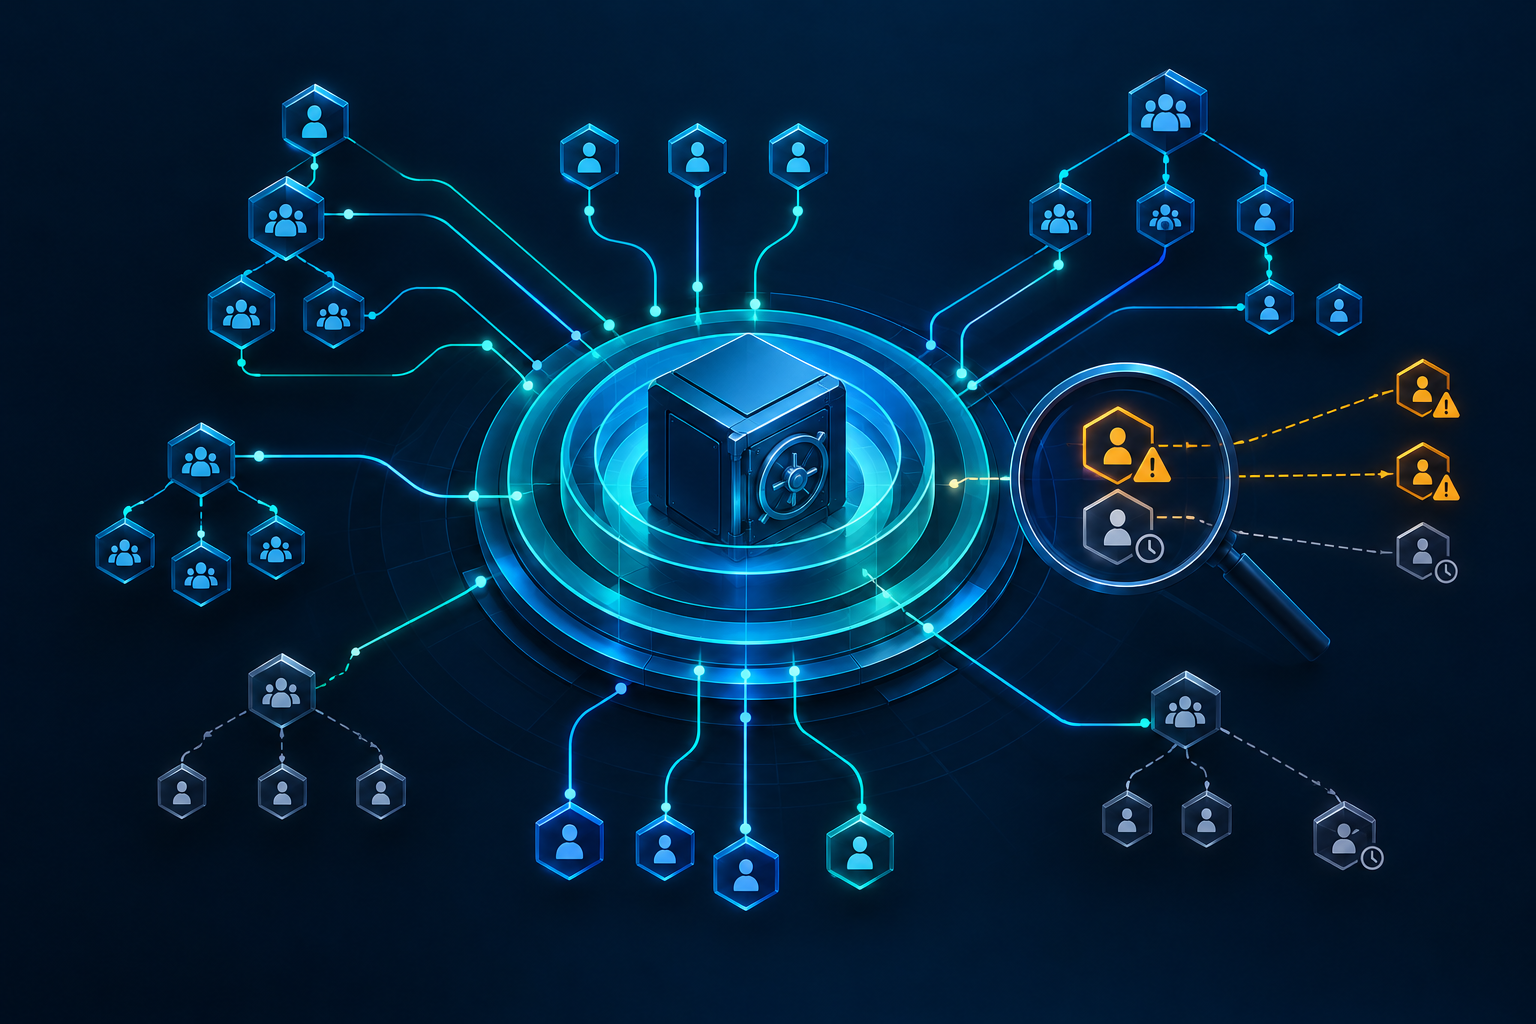
A repository permission review should determine what each identity can actually do to compliance evidence. Exporting a list of assigned application roles is only a starting point. Effective access may also come from nested groups, cloud ownership, shared links, service tokens, inherited folders, backup administration, or emergency roles.
This workflow implements the review control within Compliance Evidence Access Governance: An Operational Guide. It fits the broader AI compliance automation guide, and Layer8 Compliance can coordinate review packets, owner decisions, exceptions, and remediation evidence across identity and repository systems.
Pair the review with monitoring for unauthorized compliance evidence deletion. Periodic certification finds accumulated access, while event monitoring catches consequential actions between review dates.
Define the review objective
State the decision the review must produce. A useful objective is:
For every in-scope human and machine identity, determine its effective evidence actions, compare them with an approved role, and retain a verified decision to keep, change, remove, or time-limit the access.
Define the review period, repositories, identity sources, evidence types, and material actions. Include read, create, replace, transform, approve, export, share, delete, restore, change retention, release holds, manage permissions, and administer logging.
Do not use read access as the only scope boundary. Approval or deletion rights over a small repository may carry more control risk than read access to a large archive.
Build the entitlement baseline
The reviewer needs a policy reference before seeing current access. For each repository class and role, document:
- Permitted actions
- Prohibited actions
- Allowed object scope
- Required employment or vendor status
- Approval authority
- Maximum duration
- Required authentication
- Segregation-of-duties constraints
- Exception process
- Evidence needed to verify removal
Map these rules to platform-specific roles, groups, API scopes, ownership permissions, and lifecycle capabilities. If a platform role is broader than policy, record the additional technical controls that constrain its use.
For example, a repository custodian may need platform administration but should not approve evidence sufficiency. If the platform bundles those actions, require independent approval records and monitor the custodian for approval events.
Inventory every access path
Collect assigned and indirect access from all relevant systems.
Human access
Include:
- Direct user grants
- Managed and unmanaged groups
- Nested group membership
- Application and cloud roles
- Folder, workspace, site, and object inheritance
- Shared links and guest accounts
- Privileged identity management eligibility
- Break-glass accounts
- Local repository accounts
- Backup, archive, and recovery administration
- Auditor portal access
- Active sessions or long-lived refresh tokens where available
A dormant account with an active token can remain capable after the directory object is disabled. Review the enforcement path, not just the directory status.
Machine access
Include:
- Service accounts
- Workload identities
- API keys and tokens
- Integration applications
- Collection agents
- Transformation pipelines
- Scheduled export jobs
- Infrastructure-as-code deployment identities
- Backup and recovery services
Record the owner, purpose, credential type, last use, permitted source, expiration or rotation policy, and exact actions. A service identity without a current owner cannot be responsibly certified.
Administrative access outside the application
Cloud resource owners, storage administrators, database administrators, encryption-key administrators, and identity administrators may be able to expose, replace, or delete evidence without appearing in the application's role export.
Model those capabilities explicitly. The review should answer who can affect the evidence, not who appears on one permissions page.
Resolve effective permissions
Normalize every access path into an identity-action-scope record. Preserve the source grant and inheritance chain.
For each identity, determine:
- Stable identity and current status
- Human, machine, guest, or emergency classification
- Source of access
- Effective role and actions
- Repository and object scope
- First grant and last change
- Last observed use
- Approver or request reference
- Expiration
- Role owner
- Conflicting or toxic combinations
Do not collapse nested access into a generic group label. The owner must see that a user can permanently delete evidence because the user belongs to a regional operations group nested inside a storage-administrator group.
Likewise, do not infer safety from lack of recent use. Unused destructive privilege is still effective privilege. Last-use data helps prioritize review but does not justify access.
Prepare a decision-ready review packet
Send each owner the minimum context needed for a reliable decision.
A practical review row contains:
- Identity and relationship to the organization
- Business owner
- Repository and evidence class
- Effective actions in plain language
- Grant path
- Approved role or policy comparison
- Last use and recent material activity
- Start date and expiration
- Existing exception
- Recommended decision and rationale
- Available decisions
Use structured decisions:
- Keep: access exactly matches a current approved role
- Modify: retain narrower scope or fewer actions
- Remove: no valid requirement exists
- Time-limit: need is valid only for a bounded period
- Exception: policy deviation is necessary and separately approved
- Investigate: owner or activity cannot yet be established
Do not provide an approve-all control for mixed entitlements. A reviewer should be able to retain read access while removing sharing or deletion capability.
Assign the right reviewers
The reviewer must understand both the business need and the effect of the permission.
Use:
- Control owners for evidence purpose and control context
- Repository owners for supported roles and object scope
- Identity owners or managers for current job need
- Security or compliance reviewers for privileged and conflicting access
- Vendor owners for external identities
- Application owners for machine identities
Self-certification is weak for privileged access. Require an independent reviewer for repository administration, retention changes, permanent deletion, hold release, permission management, and audit-log administration.
When the named owner is inactive or unknown, route the item for investigation. Do not convert missing ownership into automatic approval.
Run the review
1. Freeze the review population
Timestamp the entitlement snapshot and record collection completeness. New grants after the snapshot should enter a delta review rather than disappear until the next cycle.
2. Validate identity context
Reconcile identities with employment, vendor, application, and asset records. Identify departed users, expired guests, transferred staff, disabled services, and duplicate accounts.
3. Compare access with policy
Evaluate action, scope, duration, authentication, approval, and segregation requirements. Flag direct grants where managed roles are required and permanent privilege where just-in-time access is policy.
4. Collect accountable decisions
Require a reason for keep, modify, exception, and investigate decisions. Record the reviewer identity and decision time. Prevent the reviewed identity from approving its own privileged access.
5. Escalate nonresponse
Escalate based on risk and review deadline. For low-risk read access, temporary suspension may be appropriate after warning. For production integrations, immediate disablement can interrupt evidence collection, so use a controlled owner and risk decision.
6. Create remediation work
Translate each decision into exact technical actions. "Remove excess access" is ambiguous. State the group membership, role assignment, shared link, token, ownership right, or inherited grant that must change.
Verify remediation
Ticket closure is not enough. Collect fresh effective-access evidence after the change.
Verification should confirm:
1. The target grant was removed or changed.
2. Indirect paths do not preserve the same action.
3. Active sessions or tokens were revoked where required.
4. Downstream repositories and exports were addressed.
5. Automation still performs its approved function.
6. The identity cannot perform the prohibited action.
7. The review record links to before-and-after evidence.
8. Any exception has an owner and expiration.
Where possible, test access using policy simulation or a controlled non-production object. Avoid asking reviewers to attempt destructive actions against live evidence.
If a permission change interrupts collection or review, route the affected artifacts through Compliance Evidence Validation: An Operational Quality-Control Workflow after service is restored.
Handle common review failures
Role names hide effective actions
A role called contributor may include sharing or overwrite rights. Translate native roles into actions before review.
Group owners approve without seeing nested members
Show resolved membership and the chain that provides access. Certifying the group name alone does not review its population.
Direct and inherited grants are remediated separately
Remove all paths that provide the prohibited capability. Otherwise, the change produces a clean ticket with unchanged effective access.
Machine identities receive permanent exceptions
Treat an integration limitation as a designed control gap. Name the owner, constrain source and scope, monitor activity, rotate credentials, and set a review date.
External access expires only on paper
Configure technical expiration where supported. After the date, verify the guest, link, token, and active session no longer work.
Review evidence can be altered by reviewed administrators
Store snapshots, decisions, and verification records in an access-controlled evidence location. Use the integrity practices in How to Verify Compliance Evidence Integrity with Hashes and Immutable Versions for material review exports.
Example: inherited delete access
A control owner is expected to review and approve quarterly access evidence. The review packet shows read, comment, and approval rights, which match the role.
Effective-access resolution also finds permanent delete capability inherited from a collaboration-site owner group. The control owner joined that group during a migration and no longer needs it. The owner cannot certify the privilege because deletion is prohibited for evidence approvers.
The remediation removes the user from the site owner group and assigns a narrow evidence-review role. Verification resolves membership again, checks cloud and application permissions, revokes existing sessions, and confirms the user can approve a test record but cannot delete its underlying object. Activity records are reviewed for deletion or sharing during the period of excess access.
The root cause is role reuse: a broad migration group became a convenient way to grant routine repository access. The organization creates a dedicated reviewer group and adds a policy check that rejects evidence approvers with destructive capability.
Measure the review
Track measures that reveal control quality:
- Percentage of in-scope access paths collected successfully
- Identities without a current owner
- Direct grants outside approved roles
- Privileged access certified by an independent reviewer
- Keep decisions without a stated role match
- Modify and remove decisions awaiting execution
- Median time from decision to verified remediation
- Access that remains effective after reported removal
- Expired external or temporary access
- Repeat findings by repository, role, and grant path
- Machine identities without recent use or supported purpose
A fast review is not necessarily a good review. Completion can rise while owners approve unclear role labels. Measure effective-access coverage, decision quality, and verified change.
Conclusion
A compliance evidence repository permission review is an effective-access test, not a role-export exercise.
Define permitted actions first, inventory human and machine paths, resolve inheritance, and give accountable owners decision-ready context. Then translate decisions into exact changes and verify the resulting access independently. This workflow exposes indirect privilege and proves that remediation changed what an identity can actually do to compliance evidence.