How to Reconcile Vulnerability Scan Targets with Asset Inventory
Reconcile vulnerability scanner targets with authoritative asset inventory to find missed systems, stale records, ambiguous identities, and invalid scope.
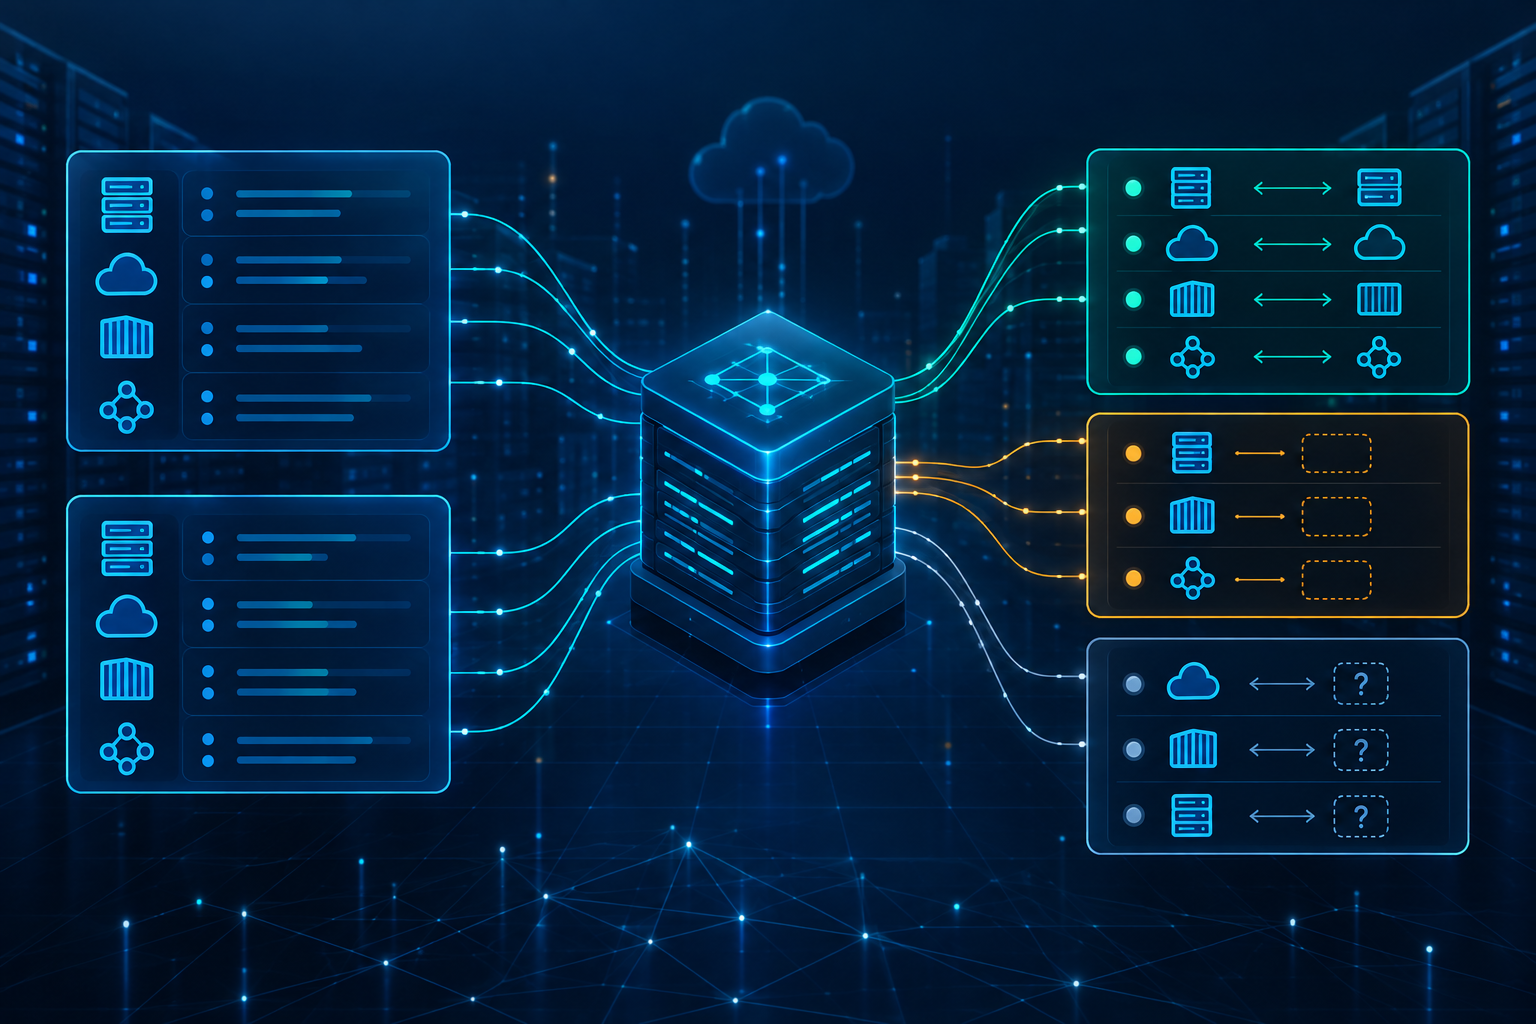
A vulnerability scanner can only assess the targets it receives. If the target set is narrower than the live environment, a clean report may simply describe an incomplete scope.
Reconciliation compares the assets that should be assessed with the targets and evidence the scanning program actually used. It finds missing systems, stale targets, identity collisions, and unsupported assumptions before those defects become coverage claims.
This workflow is a focused implementation of vulnerability scan coverage management. It fits within the complete vulnerability scanning guide and can be coordinated through Layer8 Sentinel. Teams with autoscaling, serverless, and container-heavy estates should also apply the companion method for measuring vulnerability scan coverage for ephemeral cloud assets.
Define the two populations
Reconciliation starts with two independently built sets.
Expected assets
Expected assets come from systems authorized to describe the environment. Common sources include:
- Cloud organization and account inventories
- Hypervisor and virtualization management
- Endpoint and device management
- Kubernetes control planes
- Container registries
- Configuration management
- DNS and certificate inventories
- Network source-of-truth platforms
- Service catalogs and CMDB records
- Procurement and appliance support records
An expected record should explain why the asset belongs in scope. Production status, internet exposure, critical-service membership, account placement, or a policy assignment are stronger reasons than merely appearing in an old spreadsheet.
Scan targets and evidence
The scanner side needs more than configured IP ranges. Collect:
- Target definitions
- Included and excluded ranges
- Hostnames and addresses resolved at execution time
- Asset identifiers assigned by the scanner
- Job schedules and completion states
- Per-asset reachability
- Authentication outcomes
- Inspection or check completion
- Result timestamps
- Scanner perspective or worker
- Suppressions and target-level exceptions
Configured scope shows intent. Per-asset evidence shows execution. Keep both because a correctly configured target can still fail to produce valid evidence.
Establish identity precedence
The safest reconciliation keys represent the asset itself rather than its current location.
Use a precedence model such as:
1. Cloud resource ID, hardware UUID, virtual machine UUID, or managed-device ID
2. Container image digest, cluster UID, workload UID, or application release ID
3. Authoritative fully qualified domain name with environment context
4. MAC address where its collection and lifecycle are reliable
5. IP address with observation time and network context
6. Display name or user-entered label
Do not merge records solely because they share an IP address. Address reuse can connect a current scan result to a retired system. Do not split one asset merely because its address changed.
Store the evidence behind a match. A reconciliation process should be reproducible, not a hidden fuzzy join.
Prepare the data
Normalize without destroying source values
Normalize case, whitespace, address formats, timestamps, and common identifier syntax. Preserve original values beside normalized values so analysts can investigate discrepancies.
Expand target ranges into comparable membership rules, but do not assume every address in a range represents a live expected asset. The inventory defines expected assets; a CIDR target only states where the scanner may look.
Set a common observation window
Compare records from a meaningful time interval. A current cloud inventory joined to a six-month-old scan export will produce mathematically valid but operationally useless differences.
Record:
- Inventory snapshot time
- Target configuration time
- Scan execution time
- Evidence freshness requirement
- Asset creation and retirement times
Time matters when infrastructure changes between collection points.
Separate lifecycle from coverage
An asset absent from the latest inventory is not automatically retired. Require authoritative lifecycle evidence. Similarly, an asset marked stopped may still be capable of returning to service and remain in scope.
Keep lifecycle states such as active, stopped, provisioning, draining, retired-pending-validation, and retired separate from coverage states.
Run the reconciliation
1. Match by stable identity
Join records using the highest-confidence identifiers available. Mark each deterministic one-to-one join as matched, then evaluate whether the required current scan evidence exists.
A target match alone is insufficient. The asset may be configured but unobserved, or observed without the credentialed depth required by policy.
2. Evaluate contextual matches
For records without stable shared identifiers, use combinations of hostname, address, account, subnet, operating system, owner, and observation time.
Require enough context to rule out reuse. For example, an IP and hostname observed in the same cloud account during overlapping timestamps may support a match. An IP alone, observed weeks apart, should remain unresolved.
3. Isolate ambiguous matches
Do not force many-to-one or one-to-many candidates into a convenient result. Put them in an ambiguous identity queue.
Common causes include:
- Reused hostnames
- Network address translation
- Shared load-balancer addresses
- Golden images represented as running assets
- Duplicate CMDB records
- Scanner rediscovery creating a second asset record
- Cluster nodes replaced under a naming template
- Mutable container tags
Assign the correction to the source that owns the faulty identity or lifecycle data.
4. Produce directional gaps
The comparison should produce at least four useful sets:
| Set | Interpretation |
|---|---|
| Expected and validly assessed | Current coverage evidence exists |
| Expected and targeted, but no valid evidence | Execution, reachability, authentication, or inspection failed |
| Expected but not targeted | Scope construction failed |
| Targeted or observed but not expected | Inventory may be incomplete, stale, or seeing unmanaged assets |
The fourth set matters. Scanner discovery can reveal assets absent from governance systems. Do not automatically delete them as noise.
5. Apply required scan methods
One asset may require multiple evidence paths. An internet-facing server might need an external unauthenticated assessment and an internal credentialed assessment. A Kubernetes service may require cluster configuration, image, and exposed-service evidence.
Represent each asset-method pair separately. Otherwise, one successful method can incorrectly mask a missing one.
Use credentialed scanning for hybrid environments to define host inspection requirements. For the attacker-facing view, detecting exposed services in infrastructure provides useful external scope context.
Investigate each gap
Expected but not targeted
Check whether the asset was created after target generation, placed in an unrecognized account or subnet, removed by an exclusion, or missing required classification.
Correct the source rule that builds scope. Manually adding one address may restore immediate coverage but leave the next similar asset exposed.
Targeted but not validly assessed
Determine whether the scanner attempted the asset. If it did, separate network reachability, authentication, authorization, and inspection.
The workflow for troubleshooting credentialed scan failures and coverage gaps provides a structured diagnosis. Preserve the failed attempt as evidence; do not convert it into a clean result.
Observed but not expected
Validate whether the asset is authorized. It may be a newly deployed system, shadow infrastructure, a stale scanner record, a shared service owned elsewhere, or a retired identifier reused by a different asset.
If the asset is live and in scope, add it to the authoritative source and assign ownership. If the scanner record is stale, retire it only after checking current discovery and lifecycle evidence.
Ambiguous identity
Collect evidence from the systems closest to creation: cloud activity, hypervisor events, deployment records, DHCP history, cluster state, and configuration management.
Resolve the source data, then rerun the join. Avoid maintaining permanent manual crosswalks unless they have owners and expiration dates.
Assign ownership by failed control
Route the gap to the team able to change it.
- Inventory source missing a live asset: inventory or platform owner
- Scope rule omits an eligible account: vulnerability operations
- Firewall blocks an approved scanner: network owner
- Credential fails: credential or system owner
- Required checks cannot execute: scanning engineering and system owner
- Duplicate scanner identities: scanning platform owner
- Unowned live asset: governance or service-management owner
- Unsupported asset under exception: risk owner
Layer8 Sentinel can help preserve the expected asset, failed evidence state, owner, and verification task in one operational queue without replacing the authoritative inventory or scanner.
Verify the correction
A closed reconciliation ticket should answer:
1. Is the asset present in the correct authoritative source?
2. Does it have a stable identity and owner?
3. Do scope rules select it automatically?
4. Did the intended scanner or assessment method execute?
5. Did required authentication and checks complete?
6. Is the evidence current under policy?
7. Were related assets created by the same process checked?
8. Was the temporary manual mapping or exception removed?
Use fresh scan evidence for the final decision. A configuration screenshot proves a change was attempted; it does not prove the asset was assessed.
Example: a rebuilt application tier
An application inventory lists twenty production virtual machines. The scanner reports twenty successful assets, so the initial dashboard shows complete coverage.
Reconciliation by virtual machine ID reveals a different result:
- Sixteen records match one to one.
- Two inventory assets are new replacements and have no scan evidence.
- Two scanner records belong to retired machines whose addresses were later reused.
- The matching address count stayed at twenty and hid the turnover.
The team updates target generation to consume current cloud resource IDs and account metadata. It retires the stale scanner identities, runs a targeted credentialed assessment of the replacements, and confirms all required checks. The correction applies to the deployment process, not only the two current machines.
Set the operating cadence
Run reconciliation often enough to detect change before evidence expires.
A practical cadence includes:
- Event-driven updates when assets are created or retired
- Daily comparison for internet-facing and critical environments
- Reconciliation after target, credential, or network changes
- Weekly owner-facing gap review
- Periodic source-quality review for duplicates and stale lifecycle records
Cadence should follow infrastructure velocity. A static appliance estate and an autoscaling application platform need different controls.
Conclusion
Target reconciliation prevents scan configuration from being mistaken for environmental coverage.
Build the expected and scanner populations independently, prefer stable identity, preserve time context, and keep ambiguous records unresolved until evidence supports a match. Investigate gaps in both directions and assign them to the owner of the failed control.
The result is more than a cleaner inventory. It is a defensible chain from authorized asset, to intended assessment, to current vulnerability evidence.
<!-- zero-content-links:start -->
Related Layer8 Labs guides
- Vulnerability Scan Configuration Drift Management: An Operational Guide
- How to Detect Unauthorized Vulnerability Scan Exclusions
- Explore Layer8 Sentinel
- How to Detect Silent Vulnerability Scan Failures
<!-- zero-content-links:end -->