How to Detect and Investigate Unauthorized Compliance Evidence Deletion
Detect and investigate unauthorized compliance evidence deletion by correlating activity, authorization, lineage, recovery, and downstream audit impact.
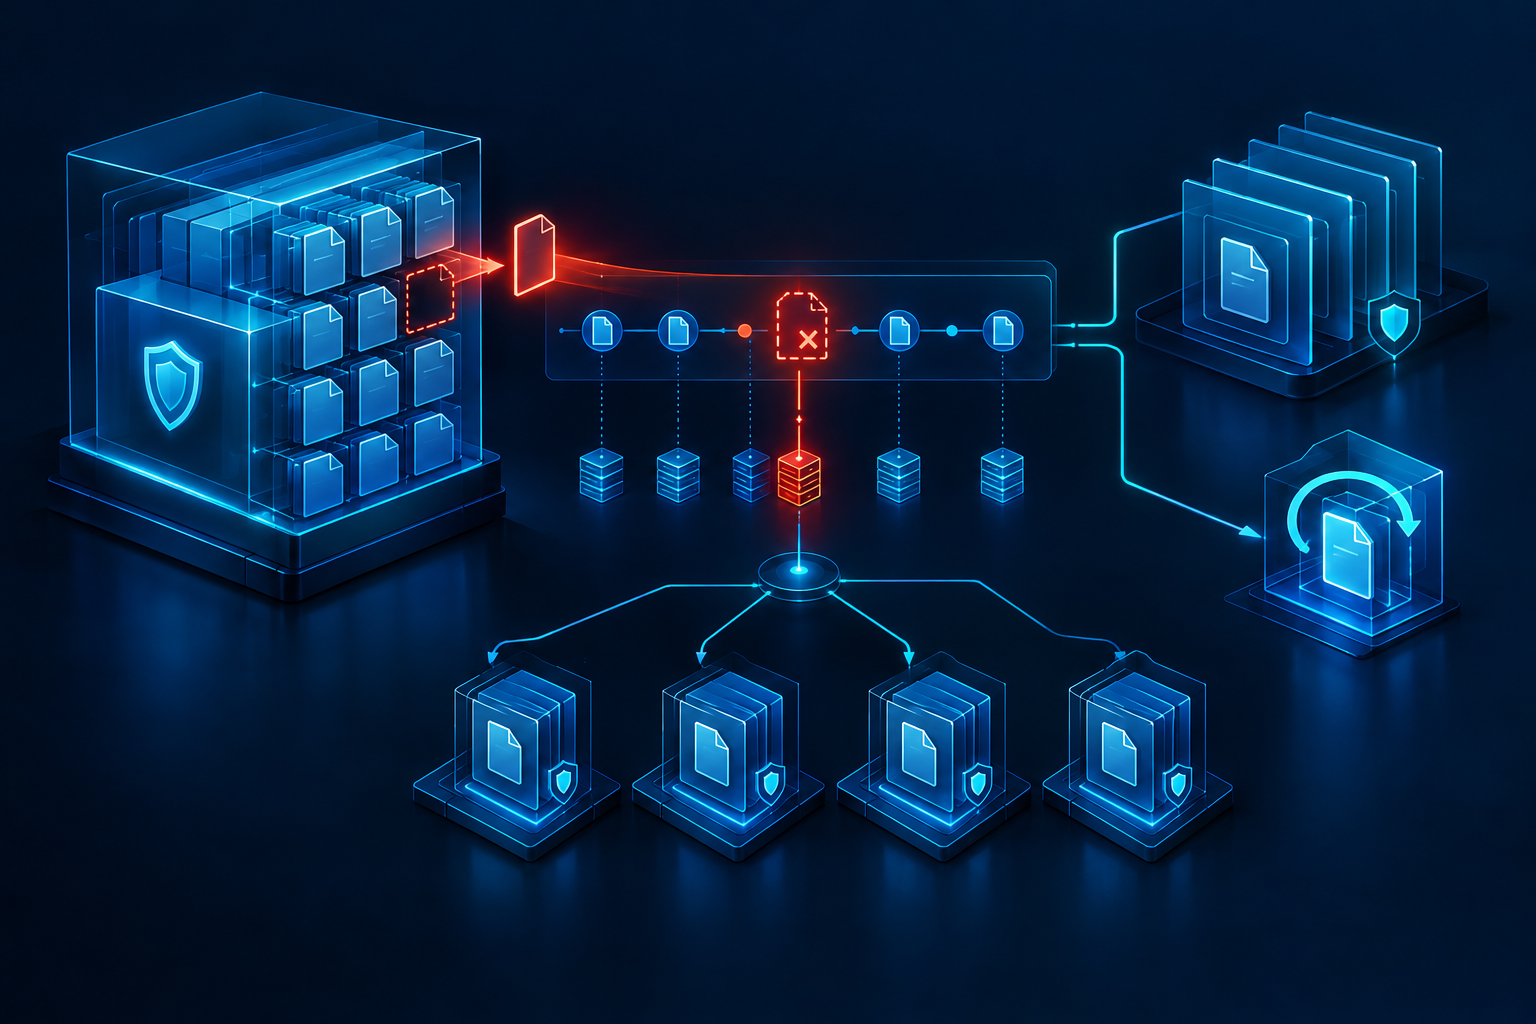
Unauthorized evidence deletion is any removal, purge, overwrite, retention change, or loss of reference that occurs outside the organization's approved evidence lifecycle. The actor may be malicious, mistaken, or operating through a poorly designed automation. The control problem is the same: required evidence became unavailable or unreliable without valid authority.
This workflow implements the destructive-action response within Compliance Evidence Access Governance: An Operational Guide. It supports the broader AI compliance automation guide, while Layer8 Compliance can correlate repository events with control records, approvals, ownership, and remediation work.
Use the companion process for reviewing compliance evidence repository permissions to find identities that retain deletion or lifecycle capability. Permission review reduces exposure; deletion detection establishes whether a specific action was authorized and what it affected.
Define deletion precisely
Repository event names vary. Monitor the effective outcomes, not only events labeled delete.
Include:
- Object or record deletion
- Permanent purge of a soft-deleted object
- Version deletion
- Overwrite that removes the reviewed version
- Bulk replacement
- Folder, workspace, site, bucket, table, or project removal
- Retention period reduction
- Lifecycle-policy changes that cause early expiration
- Legal-hold or retention-lock release
- Encryption-key deletion that makes evidence unreadable
- Reference or index deletion that makes stored evidence undiscoverable
- Source-record deletion before collection
- Backup or recovery-point deletion
- Audit-log deletion or disablement
- Integration changes that remove evidence links from control records
Distinguish content deletion from presentation changes. Removing a GRC link may leave the object intact but still break the evidence packet a reviewer used. Deleting a current object may be harmless if the governed immutable version and its references remain available. Impact depends on lineage, version, control period, and downstream use.
Establish the authorization model
Before generating alerts, define valid deletion paths.
For each evidence class, record:
- Retention and disposition rule
- Authoritative owner
- Identities allowed to request deletion
- Identities allowed to approve it
- Technical identity allowed to execute it
- Required waiting or recovery period
- Conditions that prohibit deletion
- Legal hold and investigation checks
- Required activity records
- Post-deletion verification
An action is not authorized merely because the actor had technical permission. Authorization requires a valid business rule or approved request for the exact object, action, and time.
Classify observed deletion as:
- Expected: matches approved lifecycle policy and scope
- Approved manual: supported by a valid request and authority
- Mistaken: performed by an authorized identity outside approved intent
- Unauthorized: no valid approval or policy permits the action
- Suspicious: actor, method, timing, or scale suggests misuse
- Unresolved: activity or authorization evidence is incomplete
- Apparent: object moved, reindexed, or superseded without actual destruction
Keep unresolved separate from expected. Missing logs do not prove that deletion was routine.
Collect the required telemetry
Use multiple evidence sources because the administered repository may not provide an independent record.
Collect:
- Object-level create, update, version, delete, restore, and purge events
- Identity provider authentication and risk events
- Group and role changes
- Privileged elevation records
- API gateway and application activity
- Cloud control-plane and storage data events
- GRC record and evidence-link changes
- Lifecycle, retention, backup, and legal-hold configuration changes
- Encryption-key administration
- Infrastructure-as-code changes and deployment logs
- Ticket, approval, and exception records
- Source-system history
- Centralized security logs
- Immutable version or hash manifests
Store material repository activity outside the control of routine repository administrators. An attacker or mistaken administrator should not be able to remove the evidence and the only record of its removal through the same privilege.
The provenance structure in How to Design Compliance Evidence Provenance Metadata helps connect the deleted object to its source, transformation history, control, period, reviewer, and downstream exports.
Design detection rules
Combine direct deletion events with outcome-based checks.
Direct action rules
Alert on:
- Permanent deletion or purge
- Version removal
- Bulk deletion above an environment-specific threshold
- Deletion by a reviewer, collector, or service identity that should not have the capability
- Deletion during unusual privilege elevation
- Hold release followed by deletion
- Retention reduction or lifecycle-policy expansion
- Backup or audit-log deletion
- Deletion from an unusual source, interface, or network context
- Repeated failed deletion attempts
Do not rely on one universal count threshold. One approved artifact supporting a material control can matter more than hundreds of expired temporary files.
Authorization correlation
For each action, search for a matching approved lifecycle rule or deletion request. Match exact object scope, action, actor or execution service, approval authority, and valid time window.
A ticket that says clean up old audit files should not authorize deletion across every repository. Broad or ambiguous approvals should fail correlation and require review.
Outcome and reconciliation rules
Direct logs may be incomplete. Reconcile expected evidence with current objects and references.
Detect:
- Approved evidence missing from its recorded location
- Manifest entries without available versions
- Control records whose evidence links no longer resolve
- Hash or version identifiers that changed after approval
- Evidence counts dropping without a matching disposition batch
- Source records missing before scheduled collection
- Restore points disappearing before policy permits
- Audit workspaces losing artifacts during an active engagement
The compliance evidence lineage and chain-of-custody guide provides the relationship model needed to find downstream impact.
Triage the alert
Collect enough context to prioritize without modifying the affected repository.
Capture:
- Object, version, and repository
- Event time and first detected time
- Actor and authentication context
- Access path or elevated role
- Action and interface
- Related request, policy, or deployment
- Evidence class, control, and period
- Review and approval state
- Legal hold or investigation status
- Recovery options and expiration
- Downstream packets, reports, and exports
- Similar actions in the same session or change
Prioritize based on recoverability and control impact. A permanent purge of approved evidence under legal hold is more urgent than a recoverable deletion of an unreviewed duplicate. A lifecycle change affecting future deletion may outrank one isolated event because its population continues to grow.
Run the investigation
1. Preserve independent records
Preserve centralized logs, identity events, approval records, configuration history, manifests, relevant tickets, current permissions, and available object versions. Record collection times and source identifiers.
Do not restore or recreate the artifact before preserving volatile facts if the delay does not threaten recoverability. Restoration can change timestamps, versions, links, and activity displays.
2. Confirm what happened
Determine whether the object was deleted, moved, overwritten, made inaccessible, or dereferenced. Identify every affected version and replica.
Check whether lifecycle automation, synchronization, source cleanup, or infrastructure deployment performed the action under a service identity. The visible actor may be an execution mechanism rather than the accountable requester.
3. Determine authority
Find the policy or request that could authorize the action. Verify the requestor, approver, object scope, time, legal-hold check, and execution identity.
Classify an approved administrator who deletes the wrong object as an authorized identity performing an unauthorized action. This distinction directs remediation toward both access design and process safety.
4. Establish the impact interval and population
Determine when the evidence became unavailable and when the condition was detected. Resolve related artifacts governed by the same deletion, policy, token, role, job, or deployment.
Record:
- Affected controls and periods
- Collection and approval status
- Audit or customer deliveries
- Decisions that relied on the evidence
- Available source records and replicas
- Retention or legal obligations
- Integrity records for prior versions
- Evidence that may have been deleted without a surviving manifest
Do not limit impact to the alerted object. A lifecycle rule changed today may schedule a larger population for deletion later.
5. Contain the path
Contain based on risk and recoverability.
Actions may include:
- Suspend the responsible job or token
- Remove or narrow destructive permission
- End privileged sessions
- Disable the changed lifecycle rule
- Apply a temporary retention or legal hold
- Protect remaining versions and backups
- Restrict deletion to an approved recovery service
- Preserve affected storage from further automation
- Notify control, legal, security, and audit owners
Avoid disabling a collection pipeline if doing so will create a larger evidence gap. Separate its required create function from the destructive capability where possible.
6. Recover the evidence
Recover the exact governed version where available. Preserve the recovered object's relationship to the original identity and record the recovery method.
Recovery sources may include:
- Native version history
- Soft-delete or recycle storage
- Immutable object version
- Backup or snapshot
- Source-system regeneration
- Approved audit export
- Recipient copy with verified provenance
A newly collected artifact is not always equivalent to the deleted one. If the original supported a prior review period, current source state may not reconstruct historical conditions.
7. Verify integrity and usability
Use How to Verify Compliance Evidence Integrity with Hashes and Immutable Versions to compare recovered content with manifests, immutable versions, or previously reviewed copies.
Then verify:
1. The artifact is the required version.
2. Source and provenance metadata remain intact.
3. The control and period association is correct.
4. Prior transformations and redactions are understood.
5. The reviewer decision points to the restored version.
6. Repository permissions prevent recurrence.
7. Downstream packets and links resolve correctly.
8. Retention and hold settings are restored.
9. Monitoring detects a controlled test where safe.
Route recovered or regenerated artifacts through Compliance Evidence Validation: An Operational Quality-Control Workflow. Integrity alone does not prove completeness or relevance.
Decide whether prior conclusions are affected
The investigation must state whether deletion changed only availability or also undermined prior assurance.
Possible outcomes include:
- Exact reviewed version recovered and prior conclusion remains supported
- Evidence recovered, but chain of custody requires additional review
- Equivalent evidence recollected for current state but historical support remains incomplete
- Control conclusion must be reopened
- Audit or customer delivery must be corrected
- Legal or contractual notification requires evaluation
- No governed evidence was affected
Do not let the technical recovery ticket make this decision implicitly. Assign it to the accountable control, compliance, audit, or legal owner.
Correct the root cause
Removal of one user's delete permission may be necessary but insufficient.
Common root causes include:
- Collection identity also had lifecycle administration
- Broad repository-owner roles used for routine work
- No technical expiration for elevated access
- Lifecycle policy deployed without population preview
- Weak separation between evidence approval and deletion
- Shared links or replicas outside governed retention
- Missing object-level activity records
- Approval scope too broad to correlate
- Backup administrators able to purge all recovery points
- Synchronization interpreted source deletion as a repository deletion
- Evidence links depended on mutable paths
Correct the path that allowed the event. Add scope previews, approval checks, immutable versions, independent logging, narrow roles, recovery tests, or deployment guardrails as appropriate.
Example: a synchronization job removes approved evidence
A synchronization service collects quarterly access-review exports from a collaboration site. Its configuration treats removal from the source folder as an instruction to remove the repository copy.
A control owner reorganizes the source site after the review. The service deletes 24 approved repository objects even though evidence policy requires seven-year retention. A reconciliation alert detects missing manifest entries; the repository records show the service identity as the actor.
The team preserves service logs, repository data events, the current job configuration, manifests, and the source-site history. No approved deletion exists. Investigators classify the action as unauthorized automation behavior rather than malicious activity.
Immutable versions allow recovery of all 24 objects. Hashes match the reviewed manifest, and the team restores object references to the control records. Reviewers confirm the original decisions remain supported. The integration is changed to create new versions without propagating source deletions, its delete scope is removed, and a test environment verifies the new behavior.
The incident closes only after effective permissions are re-queried, restored links are tested, a controlled source removal produces an alert without repository deletion, and the affected control owner accepts the impact assessment.
Measure deletion-control health
Track:
- Destructive actions without matched authorization
- Permanent deletions and retention reductions
- Missing expected evidence objects or references
- Time from action to detection
- Time from detection to containment
- Time remaining in the recovery window at detection
- Affected artifacts by control, period, and review state
- Percentage recovered as the exact governed version
- Restored objects awaiting integrity or quality validation
- Repeat events by identity, job, platform, or root cause
- Repositories without independent activity records
- Recovery tests completed successfully
A low deletion count does not prove effective control if object-level events are disabled or manifests are incomplete. Measure detection coverage and reconciliation quality as well as observed events.
Conclusion
Unauthorized compliance evidence deletion is an authorization, integrity, and control-impact problem, not merely a storage incident.
Define every destructive outcome, correlate actions with exact authority, preserve independent records, and resolve the complete affected population. Recover the governed version where possible, verify its integrity and usability, and explicitly decide whether prior control conclusions remain supported. Close the incident only after the destructive path is corrected and the organization has evidence that the same action will be prevented or detected.