Compliance Evidence Access Governance: An Operational Guide
Build an operational access governance model for compliance evidence repositories, including role design, destructive-action controls, reviews, and investigation evidence.
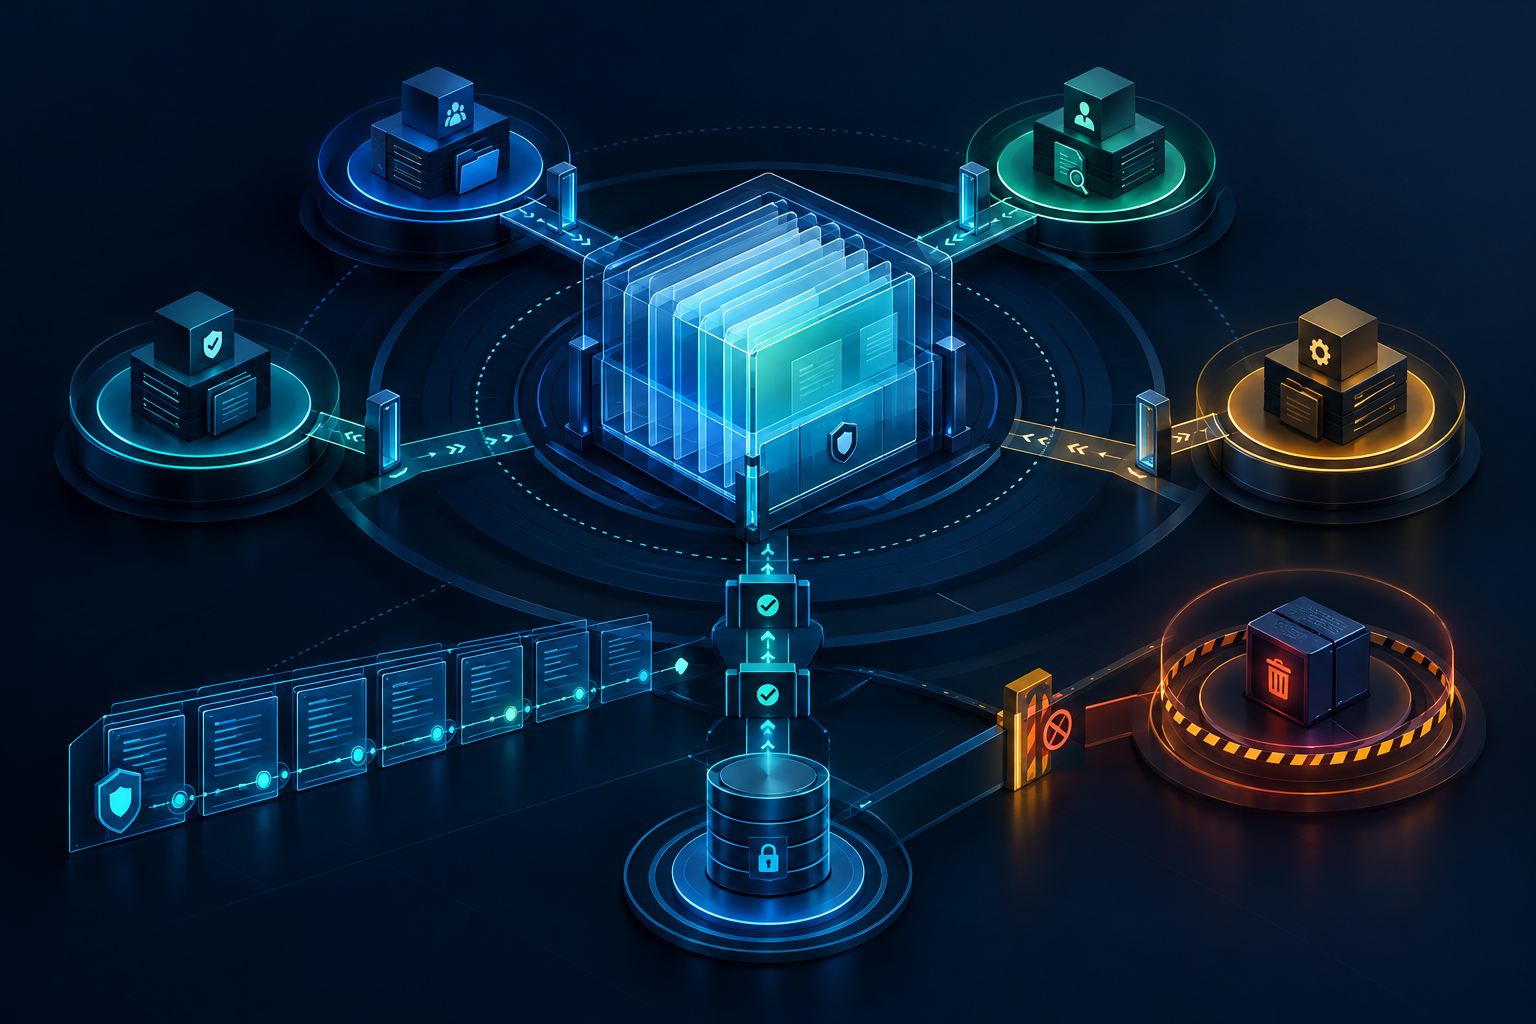
Compliance evidence is valuable because it can support a specific control conclusion. That value depends on more than collection and retention. The organization must also control who can read, add, transform, approve, export, replace, and delete the evidence.
Access governance turns those permissions into an operating control. It defines permitted actions by role, limits exceptional access, records material activity, and verifies that repository permissions continue to match policy. This guide extends the AI compliance automation guide into the evidence repository itself and shows where Layer8 Compliance can coordinate ownership, reviews, exceptions, and remediation.
The two supporting workflows address the highest-friction parts of the program: reviewing compliance evidence repository permissions and detecting unauthorized compliance evidence deletion. Use them together. A review finds accumulated privilege, while deletion monitoring identifies consequential use or abuse between review cycles.
Define the governance boundary
Start with every system that can affect the evidence presented to a reviewer. The boundary is usually wider than a GRC platform or document store.
Include:
- Source systems that generate authoritative records
- Collection identities and integration services
- Transformation or normalization pipelines
- Evidence repositories and object stores
- GRC records that reference stored artifacts
- Review, approval, and exception workflows
- Export locations and auditor portals
- Backup, archive, legal hold, and recovery systems
- Administrative consoles, APIs, and infrastructure-as-code repositories
- Logging systems that record evidence activity
An artifact can remain unchanged in its primary repository while its source record, metadata, approval status, or exported copy is altered. Model the complete path from source through audit delivery. The compliance evidence lineage and chain-of-custody guide provides the corresponding provenance model.
Define the governed object at a useful level. A repository-wide permission may affect thousands of artifacts, but the evidence record should still identify the control, period, source, version, and review state associated with each artifact. Those attributes determine whether an action is routine, prohibited, or subject to additional approval.
Build an action-based access model
Generic reader, editor, and administrator labels are often too coarse. Define access in terms of evidence actions.
Separate collection from approval
A collector may add an artifact and its source metadata. That identity should not automatically approve the artifact as sufficient. The reviewer needs authority to accept, reject, or request rework without gaining unrestricted repository administration.
Useful role boundaries include:
- Evidence producer: generates the source record
- Collector: retrieves and registers evidence
- Custodian: maintains repository availability and lifecycle configuration
- Control owner: confirms control context and responds to gaps
- Evidence reviewer: decides whether an artifact meets acceptance criteria
- Auditor or assessor: receives bounded read access
- Platform administrator: operates the supporting service
- Security investigator: accesses logs and preserved versions
- Automation identity: performs one defined machine action
One person may hold more than one role in a small organization. The control should still record which role authorized each material action and where an independent review is required.
Treat transformations as privileged actions
Normalization, redaction, format conversion, deduplication, and metadata enrichment can make evidence easier to use. They can also remove context or change meaning.
Allow transformations only through approved paths. Preserve the original, record the transformation method and version, and link the output to its input. If a reviewer cannot trace a transformed artifact back to an authoritative source, the repository has produced a convenient document rather than defensible evidence.
Use the metadata structure in How to Design Compliance Evidence Provenance Metadata to record actors, timestamps, source identifiers, versions, and transformation relationships.
Isolate destructive actions
Deletion, overwrite, version purge, retention reduction, legal-hold release, and audit-log disablement deserve stronger controls than routine additions.
Apply controls such as:
- Separate permission for destructive operations
- Just-in-time elevation with a short expiration
- Approval for bulk or permanent deletion
- Multi-party authorization for hold release or version purge
- Immutable object versions where supported
- Recovery windows appropriate to evidence obligations
- Alerts for destructive actions and failed attempts
- Independent logs stored outside the administered repository
- Restrictions on automation identities that can change lifecycle policy
A soft-delete feature helps recovery, but it does not replace authorization or monitoring. An administrator who can empty the recovery area or reduce retention still has an effective permanent-deletion path.
Establish policy before reviewing permissions
Write policy in a form that can be tested. For each role and repository class, specify:
- Permitted actions
- Prohibited actions
- Required scope boundaries
- Approval prerequisites
- Maximum access duration
- Authentication requirements
- Logging requirements
- Review frequency
- Exception authority and expiration
- Evidence required to close a violation
Avoid policies that only say access must be appropriate. A testable statement is that an external assessor receives read-only access to a named audit workspace for the engagement period, cannot export restricted artifacts, and loses access automatically on the agreed end date.
Map groups, cloud roles, application roles, API scopes, access-control lists, ownership rights, inherited permissions, and break-glass paths to these policy statements. The resulting entitlement catalog becomes the baseline for review and monitoring.
Implement the operating workflow
1. Register repositories and owners
Maintain an inventory of evidence locations, the data they contain, the authoritative owner, the technical custodian, the applicable retention class, and the identity source that controls access.
Do not omit temporary export folders or collaboration spaces. Evidence copied for an audit can become less protected than the source while remaining equally sensitive.
2. Provision from approved roles
Use managed groups or roles instead of direct grants where possible. Require a request to state the business purpose, repository scope, role, approver, start time, and expiration.
Provision automation identities for one workflow. A collection service normally needs source read access and repository create access; it rarely needs approval, policy administration, or permanent deletion.
3. Record material activity
Capture successful and failed authentication, permission changes, additions, replacements, transformations, approvals, exports, lifecycle changes, deletions, recovery actions, and logging changes.
Centralize a protected copy of these events. Repository-native logs controlled by the same administrator as the evidence do not provide independent accountability.
4. Review effective access
Run recurring reviews based on the sensitivity and change rate of the repository. Include event-driven reviews after role changes, platform migrations, acquisitions, audit completion, integration changes, and suspected compromise.
The focused repository permission review workflow explains how to resolve inherited and indirect access, collect owner decisions, and verify removal.
5. Investigate policy violations
Route prohibited or unexplained actions into a controlled investigation. Preserve logs and current configuration before changing access. Determine the affected evidence population, the actor and access path, the authorization context, and whether control conclusions or prior audit deliveries are affected.
For deletion events, follow the unauthorized evidence deletion investigation workflow so recovery does not erase the facts needed to establish impact.
6. Verify remediation
A closed ticket is not proof that access changed. Re-query effective permissions, test the prohibited action where safe, confirm temporary credentials expired, and check that downstream copies or tokens do not preserve the same capability.
When the issue affects evidence quality, route restored or recollected artifacts through Compliance Evidence Validation: An Operational Quality-Control Workflow. A recovered file may be authentic but stale, incomplete, or disconnected from its approval record.
Govern exceptional access
Emergency access is sometimes necessary to restore a failed collection, respond to litigation, or recover evidence. Make it fast and bounded.
The exceptional-access record should contain:
- The incident or business reason
- Exact identity and requested capability
- Repository and object scope
- Approver
- Start and automatic expiration
- Expected actions
- Session or activity evidence
- Post-use review owner
Alert when the access is activated, not only when it is granted. After expiration, verify removal and review activity against the stated purpose.
Do not convert a recurring operational need into repeated emergency access. If a team repeatedly needs the same capability, redesign the supported role and its controls.
Connect access governance to evidence integrity
Access governance and integrity verification answer different questions. Permissions show whether an actor could perform an action. Activity records show whether an action was observed. Hashes and immutable versions help determine whether content changed.
Use all three when material evidence is replaced or disputed. The workflow in How to Verify Compliance Evidence Integrity with Hashes and Immutable Versions can compare the reviewed version with the current or recovered object. Access and audit records then establish the path by which any difference occurred.
Do not treat a matching hash as proof that access is correct. Excessive privilege remains a control weakness even if it has not yet produced a detected modification.
Example: external audit workspace
A compliance team creates a workspace containing approved evidence for an external assessment. Reviewers publish selected artifacts from the internal repository, and the assessor receives read-only access for six weeks.
The entitlement baseline permits the assessor group to read named workspace objects but not view internal comments, upload replacements, change sharing, or export a restricted customer-data subset. Publication automation can create new immutable versions but cannot approve them. A compliance manager approves publication, while a separate repository custodian manages retention.
A permission review finds that one former assessor still has access through a collaboration group. The team removes the membership, verifies effective access, revokes an active session, and searches activity records for use after the engagement ended. No activity is found. The root cause is an external group without automated expiration, so the team replaces direct group lifecycle management with engagement-bound access packages.
Later, an approved artifact is deleted from the workspace by a support administrator troubleshooting synchronization. The deletion alert identifies the actor and object version. The team preserves logs, confirms the internal approved version remains intact, restores the workspace object, verifies its hash and metadata, and records the incident as an authorized identity using an unauthorized action. The access model is then changed so support can retry synchronization without deleting published evidence.
Measure control health
Use measures that identify work, not merely activity volume:
- Repositories without named owners or entitlement baselines
- Direct grants outside managed roles
- Privileged identities with permanent access
- External access past its expiration
- Destructive capabilities by role and repository
- Unresolved permission-review decisions
- Time from approved removal to verified revocation
- Material actions without a valid request or workflow
- Failed destructive-action attempts
- Deleted or replaced artifacts awaiting impact review
- Recurring violations by access path or platform control
Interpret the measures in context. A rise in detected violations may reflect better monitoring. A falling permission count may be meaningless if broad inherited groups remain.
Use automation with explicit decision boundaries
Automation can inventory entitlements, resolve group membership, compare access with policy, expire temporary grants, correlate actions with approvals, and assemble review packets. It should preserve the evidence behind each recommendation.
Keep accountable decisions visible. An owner should decide whether an unusual entitlement remains justified. An investigator should determine whether an action was authorized and material. Automation can route and explain the relevant facts without silently converting an anomaly into a violation or an exception.
Layer8 Compliance can coordinate these decisions across repository, identity, ticketing, and evidence systems while maintaining links to source records. The control design still belongs to the organization: authoritative owners, permitted actions, approval boundaries, and remediation evidence must be explicit.
Conclusion
Compliance evidence access governance protects the systems and actions that determine what reviewers can trust.
Define the full repository boundary, separate collection from approval, restrict destructive capabilities, review effective permissions, and monitor material actions between reviews. Connect every exception and remediation to verifiable evidence. The result is not simply a smaller access list; it is a defensible record of who could affect compliance evidence, what they did, why it was permitted, and how the organization responded when it was not.