Compliance Evidence Retention and Defensible Disposal: An Operational Guide
Build an operational compliance evidence lifecycle with versioned retention rules, explicit triggers, legal holds, controlled disposal, and verifiable outcomes.
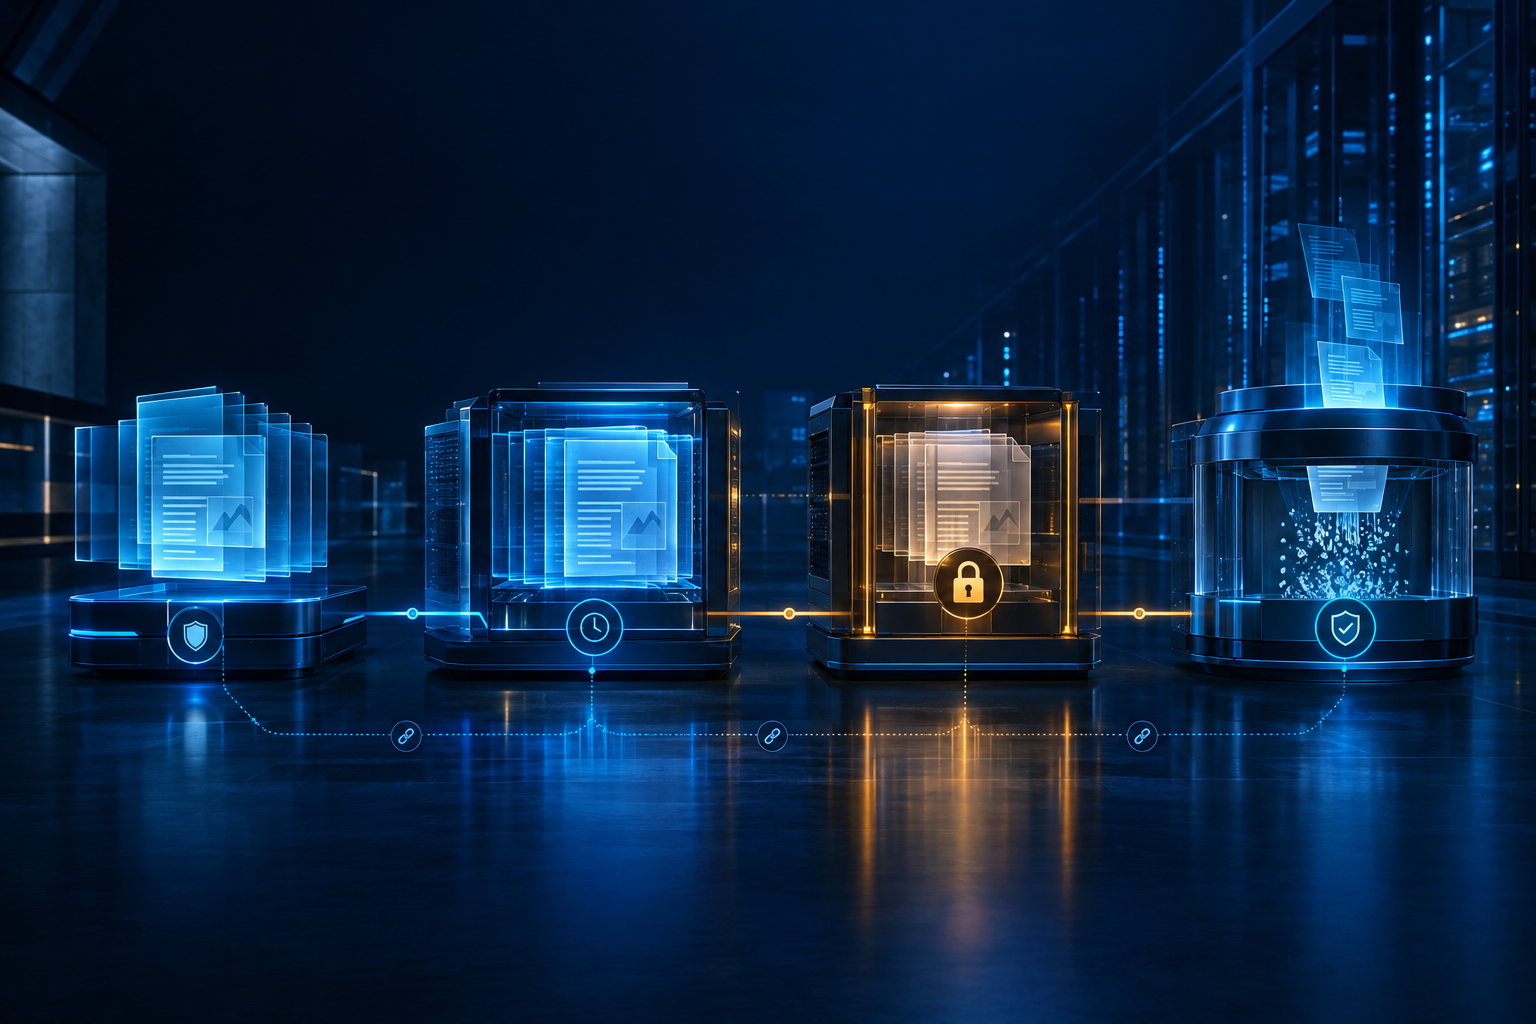
Compliance evidence does not remain useful merely because it was collected. It must stay available for the required period, remain bound to its control and decision context, survive holds and investigations, and reach an authorized end of life. Keeping everything forever is not a defensible substitute. It increases sensitive-data exposure, obscures authoritative records, and makes disposal impossible to prove.
A workable retention program treats every artifact as a governed record with a defined retention trigger, owner, preservation state, and disposal outcome. That operating model extends the evidence lifecycle described in the AI compliance automation guide. Layer8 Compliance can coordinate evidence, ownership, exceptions, and review work, but the organization still needs explicit rules for when records begin aging and who can stop their deletion.
This guide defines that operating model. The companion workflows explain how to set evidence retention rules by control and artifact and how to execute and prove authorized evidence disposal.
Define the objective before selecting storage settings
The objective is not to maximize storage duration. It is to preserve the right evidence for the right period and dispose of it only when every applicable obligation has ended.
A defensible program should answer:
- Which control, system, period, and decision does this artifact support?
- Which policy, contract, framework, or investigation requirement applies?
- What event starts the retention clock?
- Can another obligation extend the period?
- Is a hold active?
- Who can approve disposal?
- What proof shows that deletion completed across primary, replica, export, and recovery locations?
- Which minimal records must remain after content is deleted to prove the action?
Those questions establish a control boundary. Bucket lifecycle settings, ticket due dates, and document labels are implementations of that boundary, not the policy itself.
Build a retention record for every evidence class
Define retention at the evidence-class level, then bind each collected artifact to the correct class and rule version. Useful classes include access reviews, change approvals, deployment evidence, vulnerability results, policy attestations, exception decisions, control-test workpapers, and audit exports.
For each class, record:
- Evidence-class identifier and description
- Applicable control and system scope
- Record owner and technical custodian
- Data classification
- Authoritative source and governed copies
- Retention trigger
- Minimum and maximum period
- Hold eligibility
- Disposal method
- Required approval
- Rule version and effective date
The provenance model in How to Design Compliance Evidence Provenance Metadata provides the identity and lineage fields needed to connect an artifact to this record. Without stable identity, a lifecycle engine can delete the wrong copy or leave an untracked export behind.
Choose the correct retention trigger
A duration without a trigger is ambiguous. “Retain for three years” can produce several deletion dates depending on whether aging begins at collection, control execution, period close, supersession, contract termination, or audit completion.
Use the event that corresponds to the obligation. Examples include:
- A quarterly access review: the end of the review period
- A policy attestation: the attestation decision time
- A change record: production deployment or formal cancellation
- An exception: expiration or revocation, plus the required post-expiration period
- A superseded policy: the effective date of the replacement
- An audit package: formal close of the audit or review
Record both the trigger type and observed trigger time. If the triggering event has not happened, the record should remain in a waiting state rather than receiving an estimated deletion date.
Resolve overlapping obligations conservatively
One artifact may support several controls or obligations. Do not duplicate it into separate unmanaged copies or let the shortest rule win.
Calculate the effective disposition date from all active obligations:
1. Resolve the artifact to its evidence class, control mappings, systems, and entities.
2. Evaluate every applicable retention rule.
3. Calculate a candidate date for each rule from its own trigger.
4. Select the latest valid candidate date.
5. Block disposition while any trigger is unresolved or any hold is active.
6. retain the calculation inputs, rule versions, and outcome.
Keep “minimum retention” separate from “maximum retention.” A minimum prevents premature deletion. A maximum creates a duty to dispose unless a documented obligation or hold permits continued storage.
Preserve lineage across transformations and exports
Evidence often moves through collection, normalization, review, packaging, and export. Each transformation can create another governed copy.
The compliance evidence lineage and chain-of-custody guide explains how to preserve source and transformation relationships. Apply retention decisions through that graph:
- Identify the authoritative source record.
- Register normalized and redacted derivatives.
- Associate audit packages with their component evidence.
- Record exports and temporary reviewer copies.
- Distinguish independently governed records from reproducible caches.
- Propagate holds to copies that contain the affected evidence.
Do not assume deleting a pointer deletes its target, or that deleting a source safely removes a package containing the same content.
Separate preservation from access
A preserved record does not need to remain broadly accessible. Retention and access are independent control decisions.
Move aging evidence to a controlled tier when appropriate, but preserve:
- Readability
- Integrity
- Identity
- Searchability by authorized custodians
- Hold enforcement
- Access logging
- Documented recovery procedures
Apply the least-privilege model from Compliance Evidence Access Governance: An Operational Guide. Restrict archived evidence to custodians and approved reviewers. A retention obligation does not justify standing access for every former collaborator.
Make holds explicit workflow states
A hold suspends normal disposal for a defined population. It should not be a label applied manually to whichever files someone happens to find.
A hold record should include:
- Authority and reason
- Requestor and accountable owner
- Scope criteria
- Start time
- Affected systems and evidence classes
- Custodian acknowledgments where needed
- Review cadence
- Release authority
- Release time and follow-up disposition calculation
Resolve the scope against evidence metadata and lineage. New artifacts entering the scope after the hold begins must also be preserved. Test the hold by selecting representative records and confirming that scheduled lifecycle actions are blocked.
When a hold is released, do not delete everything immediately. Recalculate each artifact against its remaining obligations and route only eligible records into the controlled evidence disposal workflow.
Control lifecycle changes
A retention-rule change can alter thousands of disposition dates. Treat it as a controlled production change.
Require:
1. Proposed rule and rationale
2. Affected evidence classes and populations
3. Comparison with the current rule
4. Review by compliance, legal, security, privacy, and system owners as applicable
5. Bounded impact preview
6. Approval and effective date
7. Versioned deployment
8. Post-deployment reconciliation
9. Rollback or correction path
Do not apply a shorter period retroactively without reviewing records that would become immediately eligible. Quarantine that population for a second decision before deletion.
Reconcile policy with storage behavior
Policy is only effective when storage systems enforce it. Build a recurring reconciliation between expected lifecycle state and actual state.
For each governed repository, compare:
- Records expected to be present
- Records expected to be on hold
- Records expected to be eligible for disposal
- Lifecycle configuration and version
- Completed deletion events
- Failed or delayed actions
- Unregistered exports and replicas
- Records retained beyond their authorized date
The denominator discipline in Compliance Evidence Coverage Monitoring: An Operational Guide is useful here. Define the expected population from authoritative evidence records, not from whatever files a repository happens to list.
Handle exceptions without weakening the rule
Operational constraints can delay disposal: immutable storage windows, backup rotation, platform limitations, an unavailable owner, or an investigation into a failed deletion. Represent these as time-bound exceptions.
Each exception should state:
- Exact affected records and locations
- Constraint
- Risk
- Owner
- Approver
- Compensating controls
- Expiration
- Required remediation
- Verification evidence
An exception changes the authorized workflow for a bounded population. It must not silently rewrite the retention rule.
Measure control health
Useful measures describe whether the lifecycle is working:
- Artifacts mapped to a current retention rule
- Artifacts with unresolved triggers
- Active holds without current review
- Eligible records awaiting disposal
- Disposal actions failed by repository or method
- Records retained beyond maximum authorization
- Unregistered copies discovered
- Sampled deletions verified across required locations
- Rule changes awaiting impact review
Every measure should resolve to records. Avoid a single “retention compliance” percentage that combines missing metadata, overdue disposal, active holds, and platform failures.
Example: quarterly access-review evidence
A quarterly access review produces a source export, reviewer decisions, exception records, remediation tickets, and a signed completion record.
The team classifies the completion record and reviewer decisions as authoritative evidence. The source export is a governed input. Temporary working files are registered as derivatives with a shorter maximum life.
The retention clock begins at quarter close. A contractual obligation extends the normal policy for one business unit, so the effective date uses the longer requirement. An investigation hold later covers two applications and propagates to their evidence and package derivatives.
At hold release, the system recalculates dates. Eligible temporary files enter disposal; the authoritative review evidence remains. The team validates the batch with the evidence integrity workflow before disposition and retains a non-content disposal record showing scope, approval, method, result, and exceptions.
Implementation sequence
Start with one bounded evidence domain:
1. Inventory repositories and evidence classes.
2. Define rule records and trigger semantics.
3. Add retention metadata during collection.
4. Map copies and transformations through lineage.
5. Implement hold creation, testing, review, and release.
6. Preview disposition candidates without deleting them.
7. Approve and execute a small disposal batch.
8. Verify deletion and preserve the disposal record.
9. Reconcile the repository against expected state.
10. Expand only after exceptions and failures are understood.
The retention-rule design workflow should be complete before automated disposal begins. The disposal workflow then converts eligibility into a controlled, reviewable action.
Conclusion
Compliance evidence retention is an evidence-lifecycle control, not a storage preference. A defensible program connects each artifact to a versioned rule, starts aging from an explicit event, resolves overlapping obligations, propagates holds through lineage, restricts archived access, and proves authorized disposal.
Begin with a bounded evidence class and a dry-run disposition queue. Once the team can explain why every record is present, preserved, eligible, or disposed, automation can scale the process without hiding its decisions.
<!-- zero-content-links:start -->
Related Layer8 Labs guides
<!-- zero-content-links:end -->