How to Escalate Overdue Compliance Control Tasks in ServiceNow with AI
Build risk-based ServiceNow escalation for late attestations, evidence requests, exceptions, and remediation without relying on reminder noise.
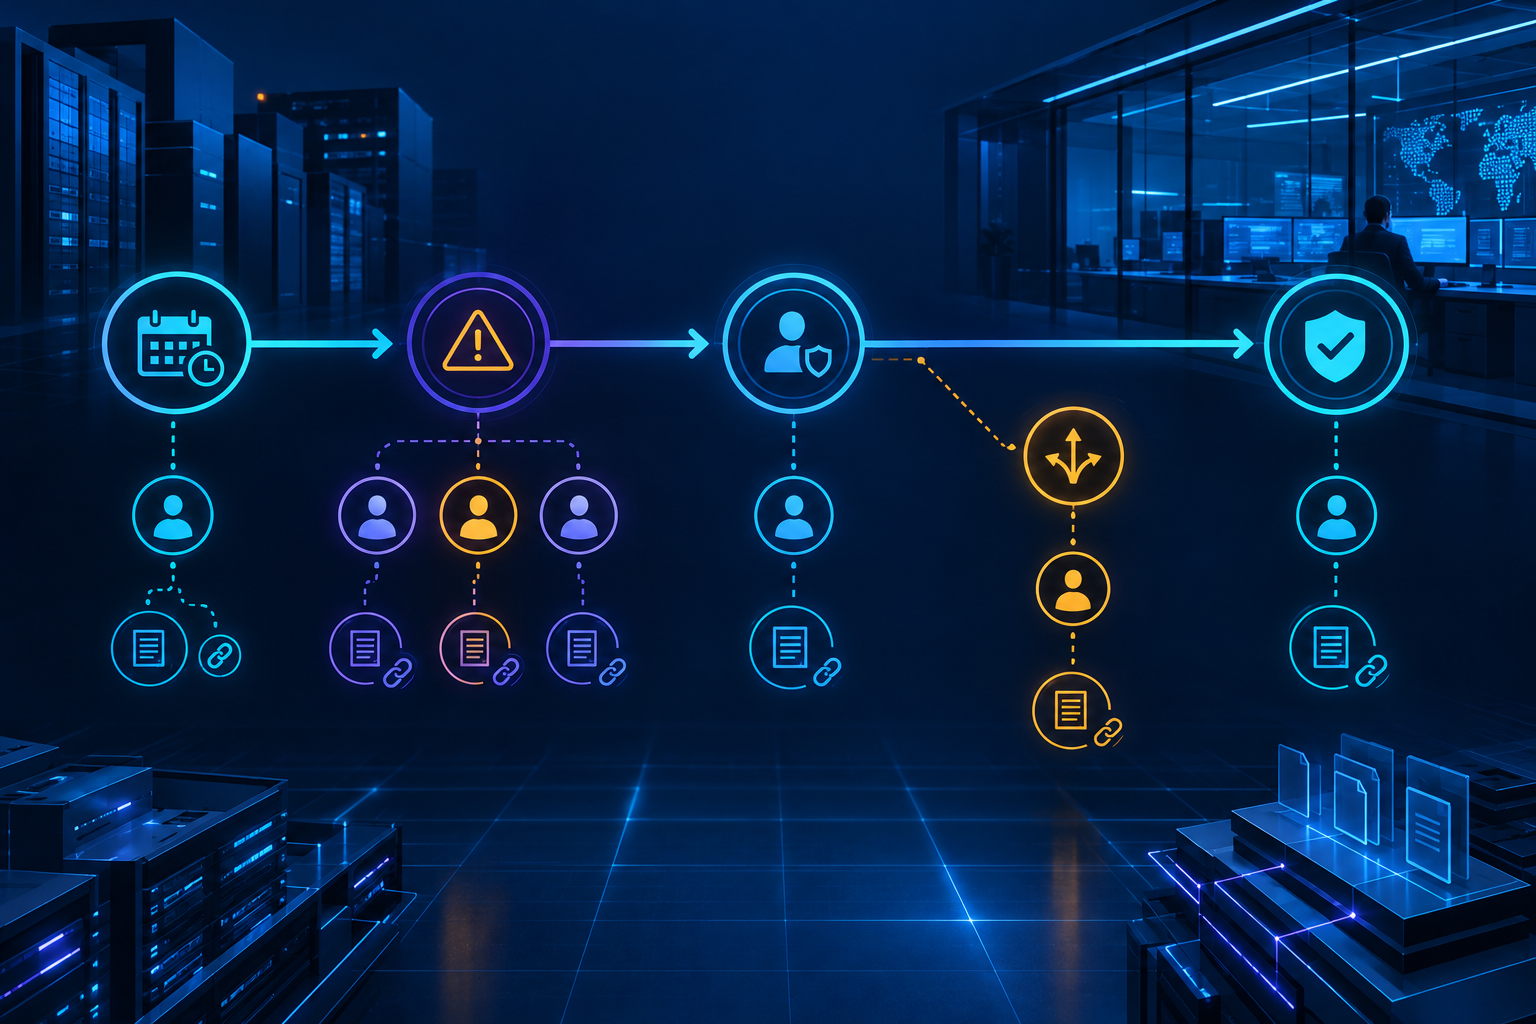
A daily reminder does not make an overdue compliance task governed.
When evidence requests, control attestations, exception reviews, or remediation items miss their dates, many programs send the same notification repeatedly. The message gets ignored, managers lack context, and the compliance team eventually escalates through a separate spreadsheet or chat thread.
ServiceNow can turn lateness into a controlled workflow. The design needs explicit clocks, risk-based thresholds, verified ownership, an exception path, and closure evidence.
This article implements the escalation layer from How to Automate Compliance Control Ownership and Attestations with AI and the broader AI Compliance Automation Guide. For the upstream review process, see How to Automate Quarterly SOC 2 Control Owner Attestations in Jira with AI.
Define what is actually overdue
A task is overdue when its governed due date has passed and no accepted terminal state or approved extension applies.
That definition requires more than comparing two timestamps. Store:
- Task type
- Related control and framework scope
- Risk tier or materiality
- Accountable owner
- Work owner
- Opened, due, and completed timestamps
- Current state
- Dependency or blocked reason
- Exception or extension record
- Escalation stage
- Last material activity
- Required closure evidence
Separate the due date from the service target. A team may target evidence collection within five business days while policy allows ten. The earlier target supports operations; the policy deadline determines a formal breach.
Do not automatically pause the clock because a task is marked blocked. Require the blocker, dependency owner, expected resolution date, and approving authority.
Classify task types before setting thresholds
Different compliance work needs different clocks.
Evidence requests
The owner must provide a defined artifact or source reference. Escalation should account for the control review date the evidence supports.
Control attestations
The accountable owner must make a decision. Delegation and ownership changes require separate validation.
Remediation
The work corrects a failed or deficient control. Severity, exposure, and compensating controls should influence escalation.
Exception reviews
The approving authority must accept, reject, modify, or expire the exception. An unanswered review should not become passive approval.
Validation tasks
A reviewer confirms that remediation or an evidence gap is actually resolved. Completion by the implementer does not close independent validation when policy requires it.
This structure aligns with How to Track and Remediate Failed Compliance Controls Using AI: every finding needs accountable assignment, a due date, and proof of closure.
Build the ServiceNow data model
Use a parent control issue or compliance case with linked work items. Each task should inherit the control, service, framework mapping, and risk context while retaining its own owner and deadline.
Create reference relationships for:
- Control
- Evidence request
- Attestation
- Deficiency or finding
- Remediation task
- Exception
- Validation task
- Audit request
Avoid copying status between records as free text. The relationships should allow ServiceNow to answer which open work prevents a control issue from closing.
Create a risk-based escalation ladder
A practical ladder has defined entry and exit conditions.
Stage 0: pre-due warning
Notify the work owner before the due date with the required outcome, current blockers, and source links. Suppress the warning if the task is already complete or has an approved extension.
Stage 1: owner escalation
When the due date passes, notify the work owner and accountable control owner. Create an escalation event with the time, reason, and delivery result.
Stage 2: management escalation
After the configured threshold, route to the owner’s manager or service owner. Include the control impact, aging, prior actions, blocked reason, and nearest audit or review dependency.
Stage 3: compliance review
For continued delay, create a compliance review decision. The reviewer can require immediate action, approve a bounded exception, change ownership, or escalate the risk.
Stage 4: risk acceptance or executive escalation
Use this stage for material or persistent items according to policy. Identify the authority allowed to accept the residual risk. Silence is not acceptance.
Risk tier should affect timing. A high-risk failed control may enter management escalation immediately, while a low-risk documentation request may have a longer operational window.
Configure the workflow
Step 1: calculate the governed clock
Apply the correct calendar, time zone, review cadence, and policy deadline. Store the calculated due date and the rule version that produced it.
If the rule changes later, do not silently rewrite historical deadlines. Record an approved recalculation with a reason.
Step 2: verify ownership
Check the assigned identity before sending escalation. If the user is inactive or no longer holds the expected role, route an ownership exception rather than filling a dead inbox with notices.
AI can suggest a likely replacement from service, team, and prior assignment context. The control program owner confirms reassignment.
Step 3: evaluate state and dependencies
Use deterministic rules to determine whether the task is complete, overdue, paused under an approved condition, or covered by an active exception.
AI can summarize blocker notes and identify likely duplicate tasks. A human reviews ambiguous dependencies.
Step 4: open the escalation event
Record the stage, trigger, recipients, task state, risk context, and next threshold. Keep escalation events as auditable records, not only email logs.
Step 5: present useful context
Each escalation should state:
- What is due
- Why it matters to the control
- How late it is
- What evidence or action is missing
- Who owns the next step
- Which exception or dependency applies
- What happens at the next stage
This reduces the need for managers to reconstruct the issue before acting.
Step 6: process the response
Allow explicit responses such as complete work, provide evidence, correct ownership, declare dependency, request extension, request exception, or dispute classification.
Each response should route through its own validation. A requested extension is not effective until the authorized person approves it.
Step 7: verify closure
Require the expected artifact, decision, or validation result before stopping the escalation. A task moved to “resolved” without closure evidence should fail the check and reopen.
The exception path should follow How to Automate Compliance Policy Enforcement and Exception Management with AI, including scope, authority, compensating control, expiry, and review.
Example: overdue encryption remediation
A cloud storage control fails because a production bucket does not meet the organization’s encryption policy. ServiceNow opens high-risk remediation for the cloud platform owner with a five-business-day deadline.
Two days before the deadline, the workflow sends a pre-due warning. The owner records that a legacy integration blocks the change but does not identify a dependency owner or recovery date.
At the due date, the task enters Stage 1. AI summarizes the blocker and highlights the missing dependency fields. The owner identifies the application manager and requests a seven-day extension.
Because the task affects production data and no compensating control is recorded, ServiceNow routes the request to compliance review. The reviewer rejects a simple extension, approves a bounded exception with temporary access restrictions and enhanced logging, and sets an expiry date.
The remediation closes only after the encryption change is verified and the exception is retired. The record preserves the missed date, the interim risk decision, the compensating actions, and final validation.
A reminder-only workflow would show a late ticket. The governed workflow shows how the organization handled the risk.
Use AI for context, not authority
AI can help with:
- Summarizing aging work and blocker history
- Proposing task classification
- Identifying likely duplicate findings
- Suggesting the service or manager route
- Drafting a concise escalation brief
- Grouping recurring overdue patterns
- Detecting comments that imply an unrecorded dependency
Use rules for:
- Due-date calculation
- Business calendars
- Risk-tier thresholds
- Identity status
- Required approvers
- Exception validity
- Escalation stage changes
- Closure requirements
Require human authority for deadline extensions, ownership transfer, exception approval, risk acceptance, and final validation where segregation is required.
Prevent escalation noise
More notifications do not equal stronger governance.
Use these controls:
- Send only on a stage change or material state change
- Consolidate related tasks for the same owner when appropriate
- Stop notices after verified closure
- Avoid notifying managers before ownership is confirmed
- Exclude approved extensions until their revised threshold
- Reopen escalation when an exception expires
- Track failed notification delivery
- Provide one action path back to the source record
Review recurring late work by root cause. The issue may be unrealistic deadlines, broken integrations, ambiguous ownership, weak capacity, or a control design that creates work without reducing risk.
Metrics for overdue control work
Track:
- Open overdue tasks by type and risk
- Aging by escalation stage
- Time from due date to first accountable response
- Tasks assigned to inactive owners
- Extension requests and approval rate
- Exceptions created after a missed deadline
- Reopened tasks missing closure evidence
- Repeated lateness by control and service
- Time in blocked state
- High-risk items without compensating controls
Use the readiness view in How to Prepare for Compliance Audits with AI to connect those measures to upcoming audit periods and evidence requests.
How Layer8 Compliance helps
Layer8 Compliance can connect control status, evidence, attestations, findings, exceptions, and ServiceNow work items. It can summarize escalation context and detect ownership or scope inconsistencies while deterministic policy rules control deadlines and routing.
Conclusion
Overdue compliance work needs a decision path, not another reminder.
Define the governed clock, classify the task, verify ownership, and escalate by risk and state. Give managers the control context they need, route extensions and exceptions through explicit authority, and require closure evidence before stopping the workflow.
ServiceNow and AI can make escalation faster and more informative without turning a generated message into a risk decision.